SilkParasite Infrastructure: SpiceRAT Servers Tied to Energy and Government Targets Across Central Asia
SilkParasite Infrastructure: SpiceRAT Servers Tied to Energy and Government Targets Across Central Asia
Published on
Disclosure note: ahead of publishing this research on September 9, 2026, we notified the affected organizations and the relevant national CERTs, sharing a TLP:AMBER advance copy and holding publication to allow review.
The domains and certificates described here are attacker-controlled impersonations, and the affected organizations are named as apparent targets of that impersonation, not as compromised parties. Notification was made where a contact channel was available and does not imply any recipient has reviewed or confirmed these findings.
This research was carried out jointly with researcher Guy Yasur. Together, we tracked a cluster of SpiceRAT command and control servers active from late 2025 through August 2026 across a small subset of European hosting providers. A TLS certificate issued by a Chinese state-affiliated certificate authority associated with the infrastructure impersonates Uzbekistan's state railway authority. Additionally, this cluster also shares registration-level relationships with hosts Bitdefender attributed to three separate malware families in its August 19, 2026 SilkParasite report.
Detection logic built from Cisco Talos' 2024 SpiceRAT research first flagged these servers in late 2025, and in mid-March 2026, we noticed a small group of C2's coming online within days of each other. This analysis relies on internet-wide scan data, and does not address malware behavior, delivery, or initial access.
Key Findings
Shared parent domains and an identical TLS certificate connect this infrastructure to hosts Bitdefender attributed to SpiceRAT, NodeEdgeRAT, and NomadRAT, three of the seven malware families documented in the SilkParasite report.
The certificate imitating the Uzbekistan railway entity was issued by TLC, a certificate authority wholly funded by CAICT, a Chinese state research institute under the Ministry of Industry and Information Technology.
A copy of RTX Corporation's (formerly Raytheon) homepage served as default content on SpiceRAT servers, with the page hash returning only 13 IP's in a HuntSQL query, all exclusive to the cluster.
The impersonation of Uzbekistan railway also appears in Bitdefender's BloodAlchemy C2 domain, and in the certificate observed on Hunt.io's SpiceRAT servers.
Identified domains spoof named entities including Türkmengaz, the Galkynysh gas field, Tojiktelecom, and Turkmenistan's Ministry of Foreign Affairs.
Passive DNS pivots linked to this cluster show subdomain infrastructure dating to at least mid-2022, suggesting this activity has been ongoing for at least four years.
What follows examines each of these findings, beginning with the SpiceRAT servers observed prior to the SilkParasite publication.
SpiceRAT Infrastructure Predating Bitdefender's Report
Hunt.io's C2 Infrastructure module tracks servers matching detection signatures for known malware families, including SpiceRAT. In mid-March 2026, we observed a cluster of five active SpiceRAT servers: 46.30.191[.]230, 188.190.29[.]126, 193.29.59[.]159, 31.58.220[.]250, and 171.22.16[.]187. The five were active together in mid-March 2026, across multiple hosting providers and countries.
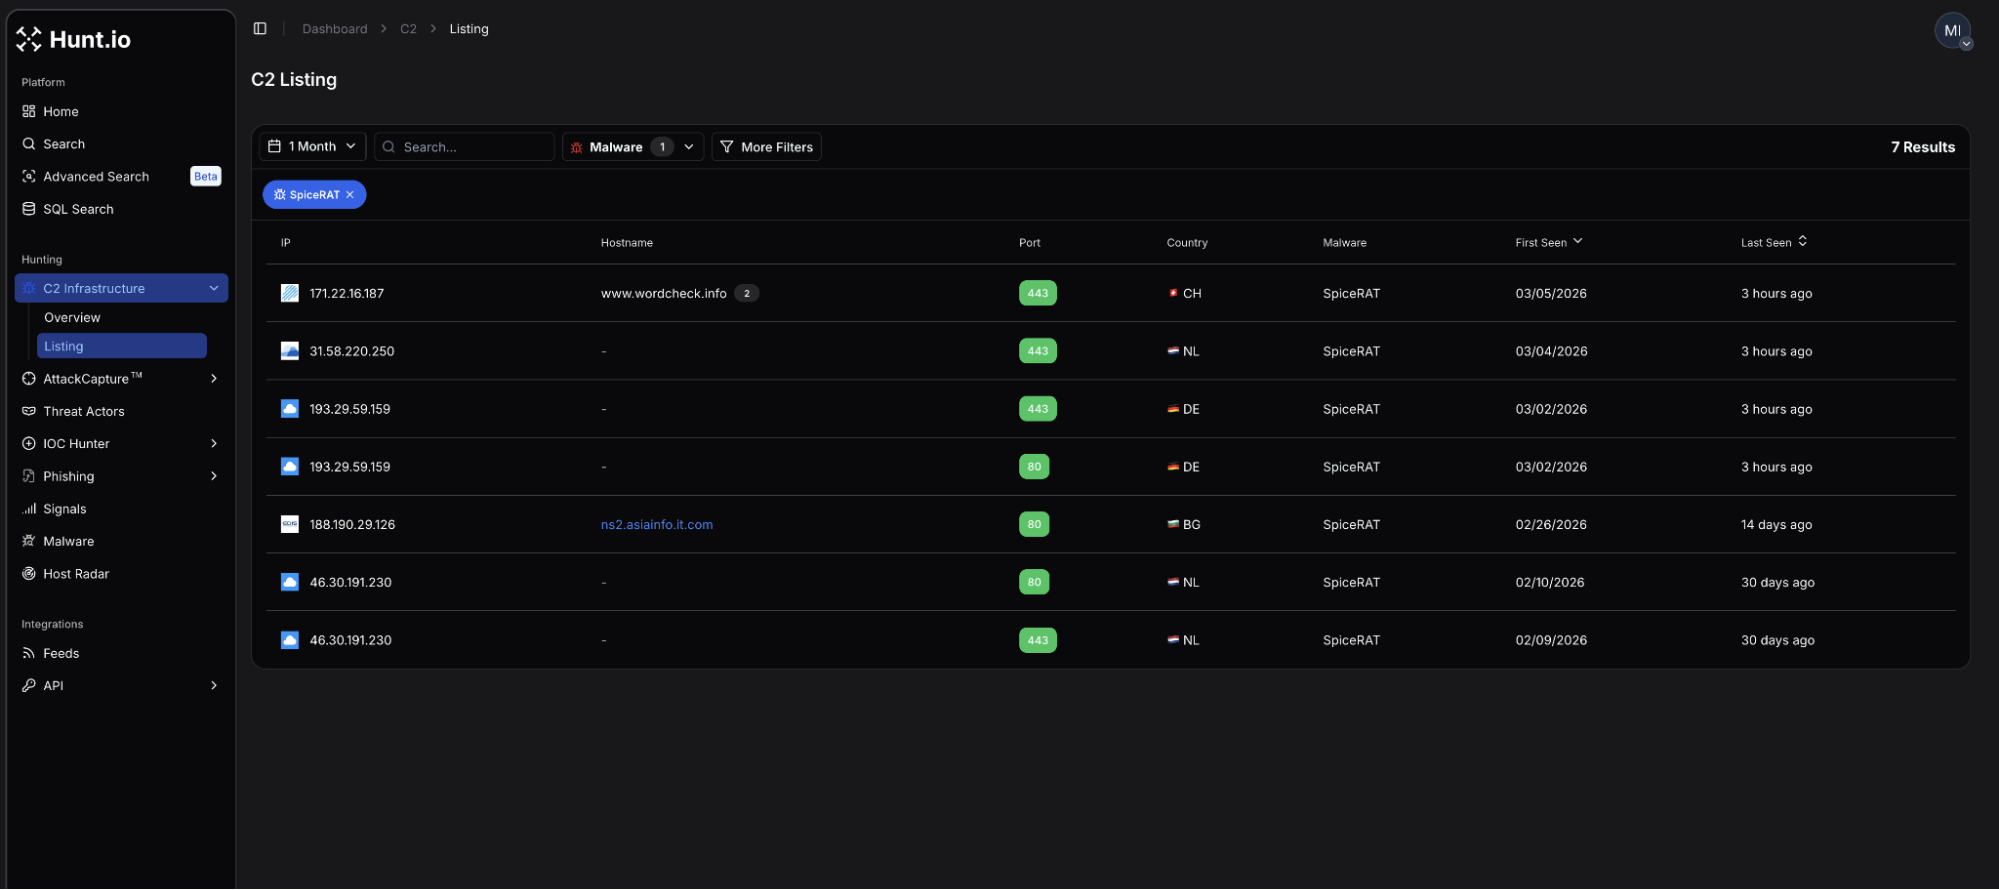 Figure 01: Historical screenshot showing a cluster of five (after deduplication) SpiceRAT servers observed in March 2026.
C2 detections establish what is running on a particular server, not who may be operating it. Grouping these hosts required a commonality, and the servers examined throughout this post are linked by at least one of three artifacts: a hostname, TLS certificate, or an identical page hash. These shared characteristics are stronger evidence of a shared operation than a shared malware family. Autonomous System (AS) names and reseller brands diverge across much of the infrastructure described in this analysis. The hosting section visited later addresses that in detail.
Hostname Reuse Across Reported and Unreported Servers
ns2.asiainfo.it[.]com resolved to three SpiceRAT servers in three different countries: 185.122.185[.]36 in Estonia on 24 January 2026, 194.71.107[.]243 in Bulgaria on 30 January, and 188.190.29[.]126 on 26 February, and where it currently resolves as of this post's publication. Each IP is hosted on a separate hosting provider network.
The Bitdefender report lists manager.skycom[.]support among its SpiceRAT indicators. The same hostname resolves to two servers absent from BitDefender's IoC list: 194.68.225[.]168 and 194.14.217[.]119, both detected in late January 2026, exposing ports 80 and 443. As of this post's publication, the domain no longer resolves to either server. Four servers published in the SilkParasite research were already flagged by Hunt.io, with the earliest dating to 2025.
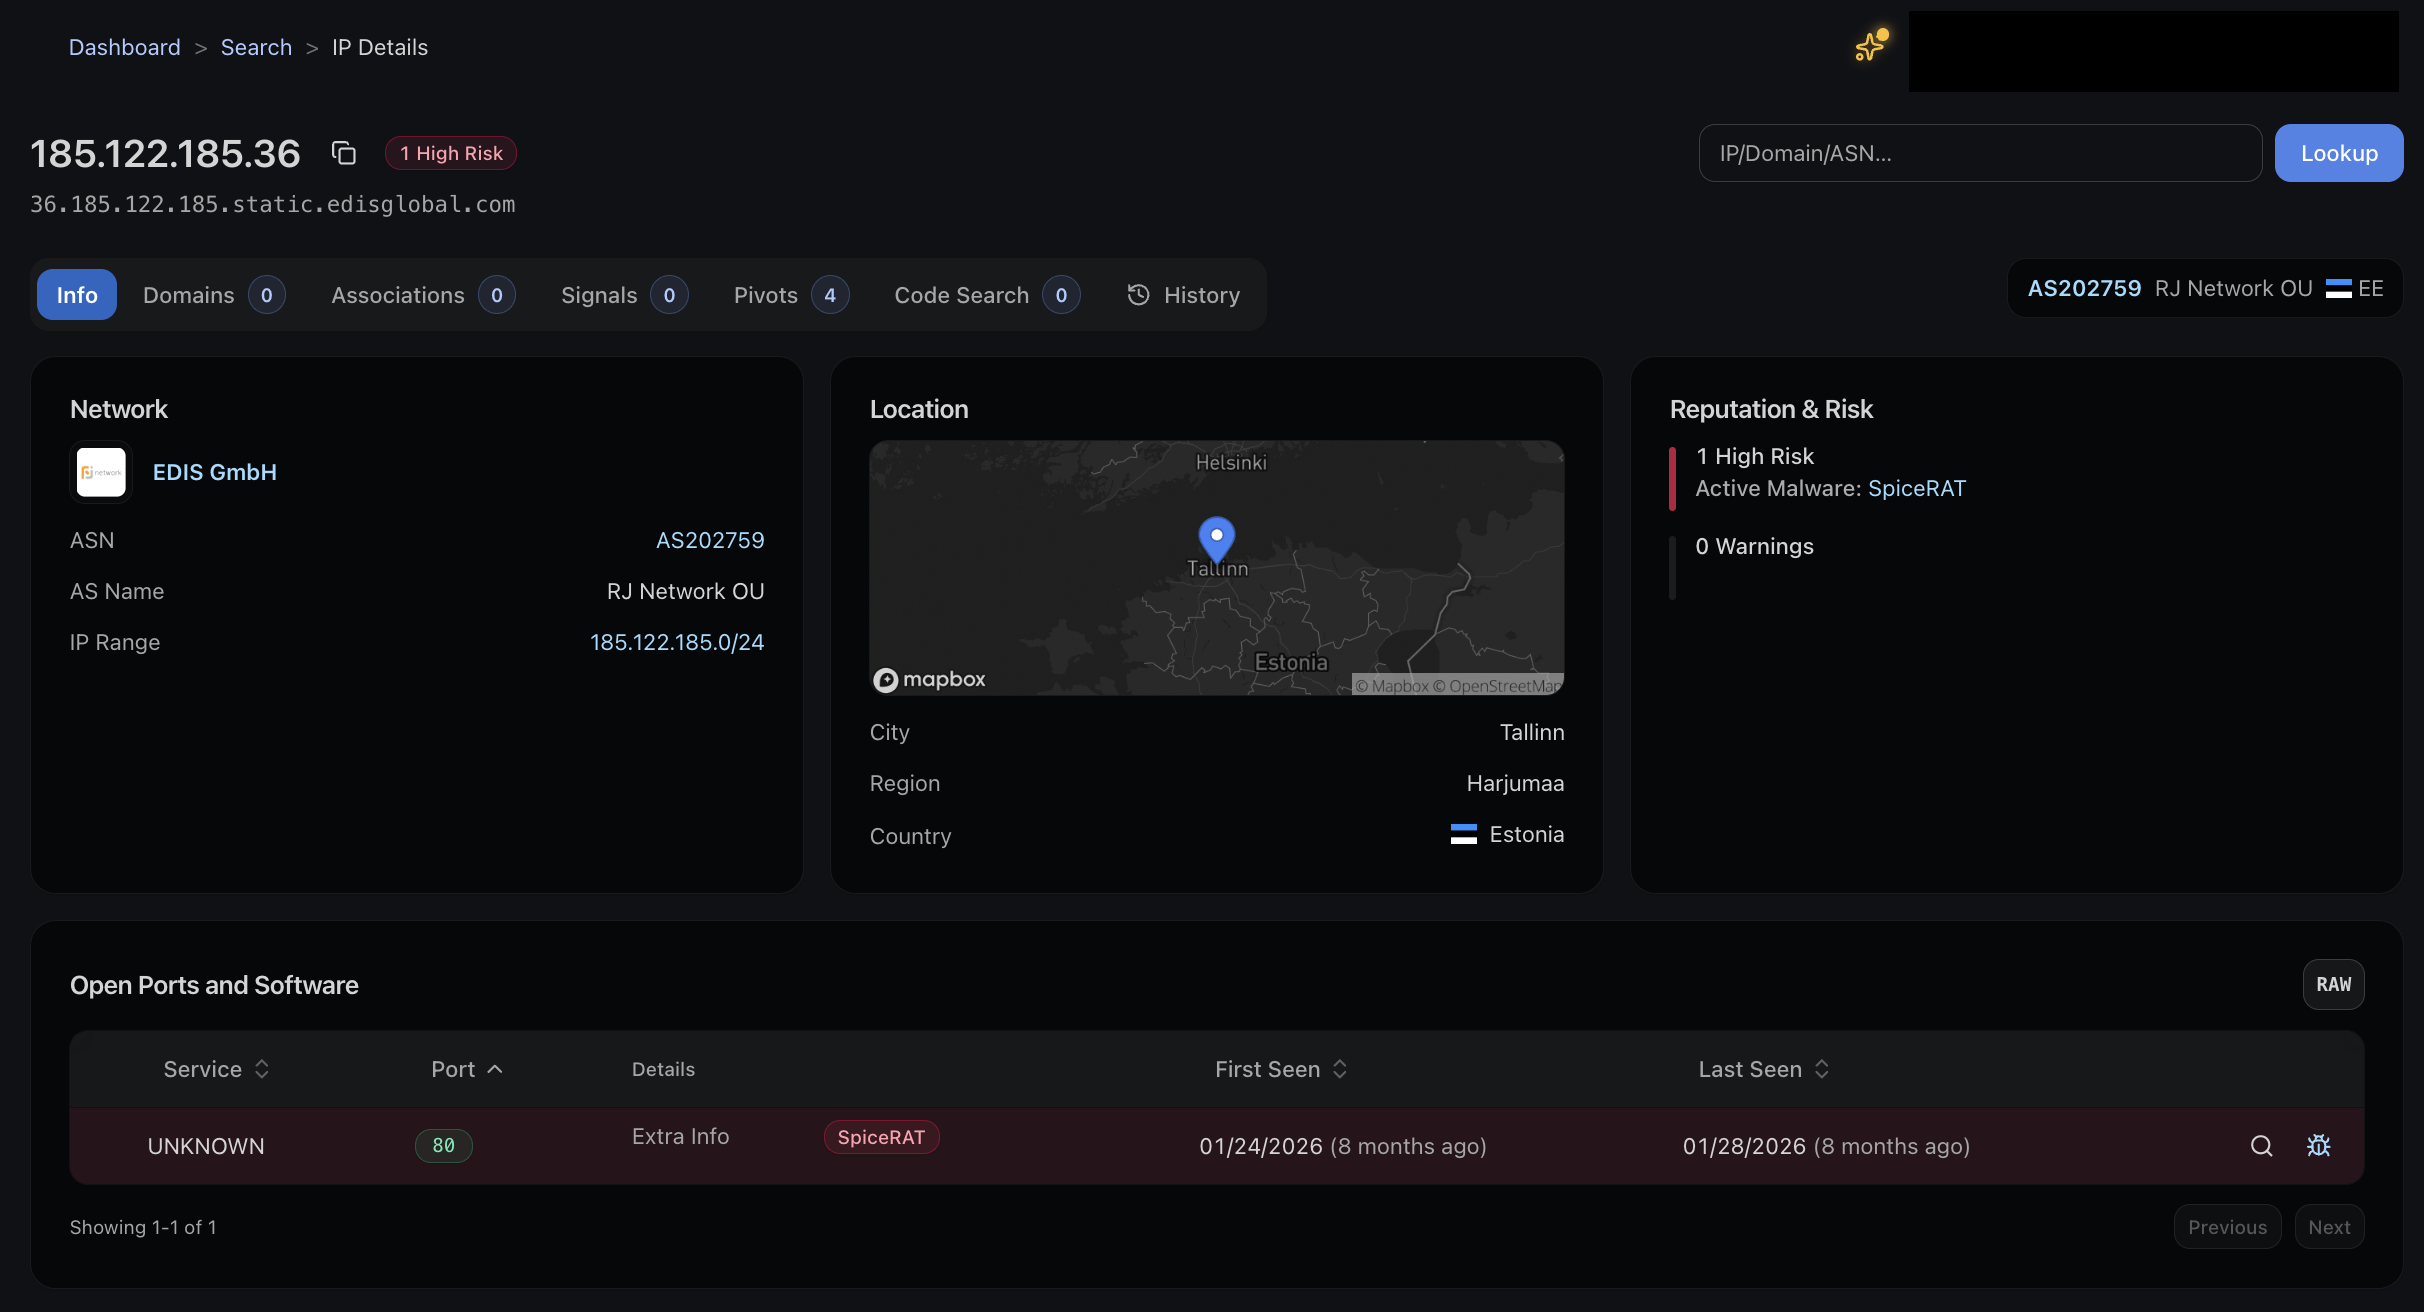 Figure 02: 185.122.185.36 IP intelligence data showing a SpiceRat detection on port 80
RTX Corporation Homepage Hosted on SpiceRAT Infrastructure
Requests to ns2.asiainfo.it[.]com on 188.190.29[.]126 returned a complete copy of RTX Corporation's homepage, including navigation, subsidiary links, and a stock ticker.
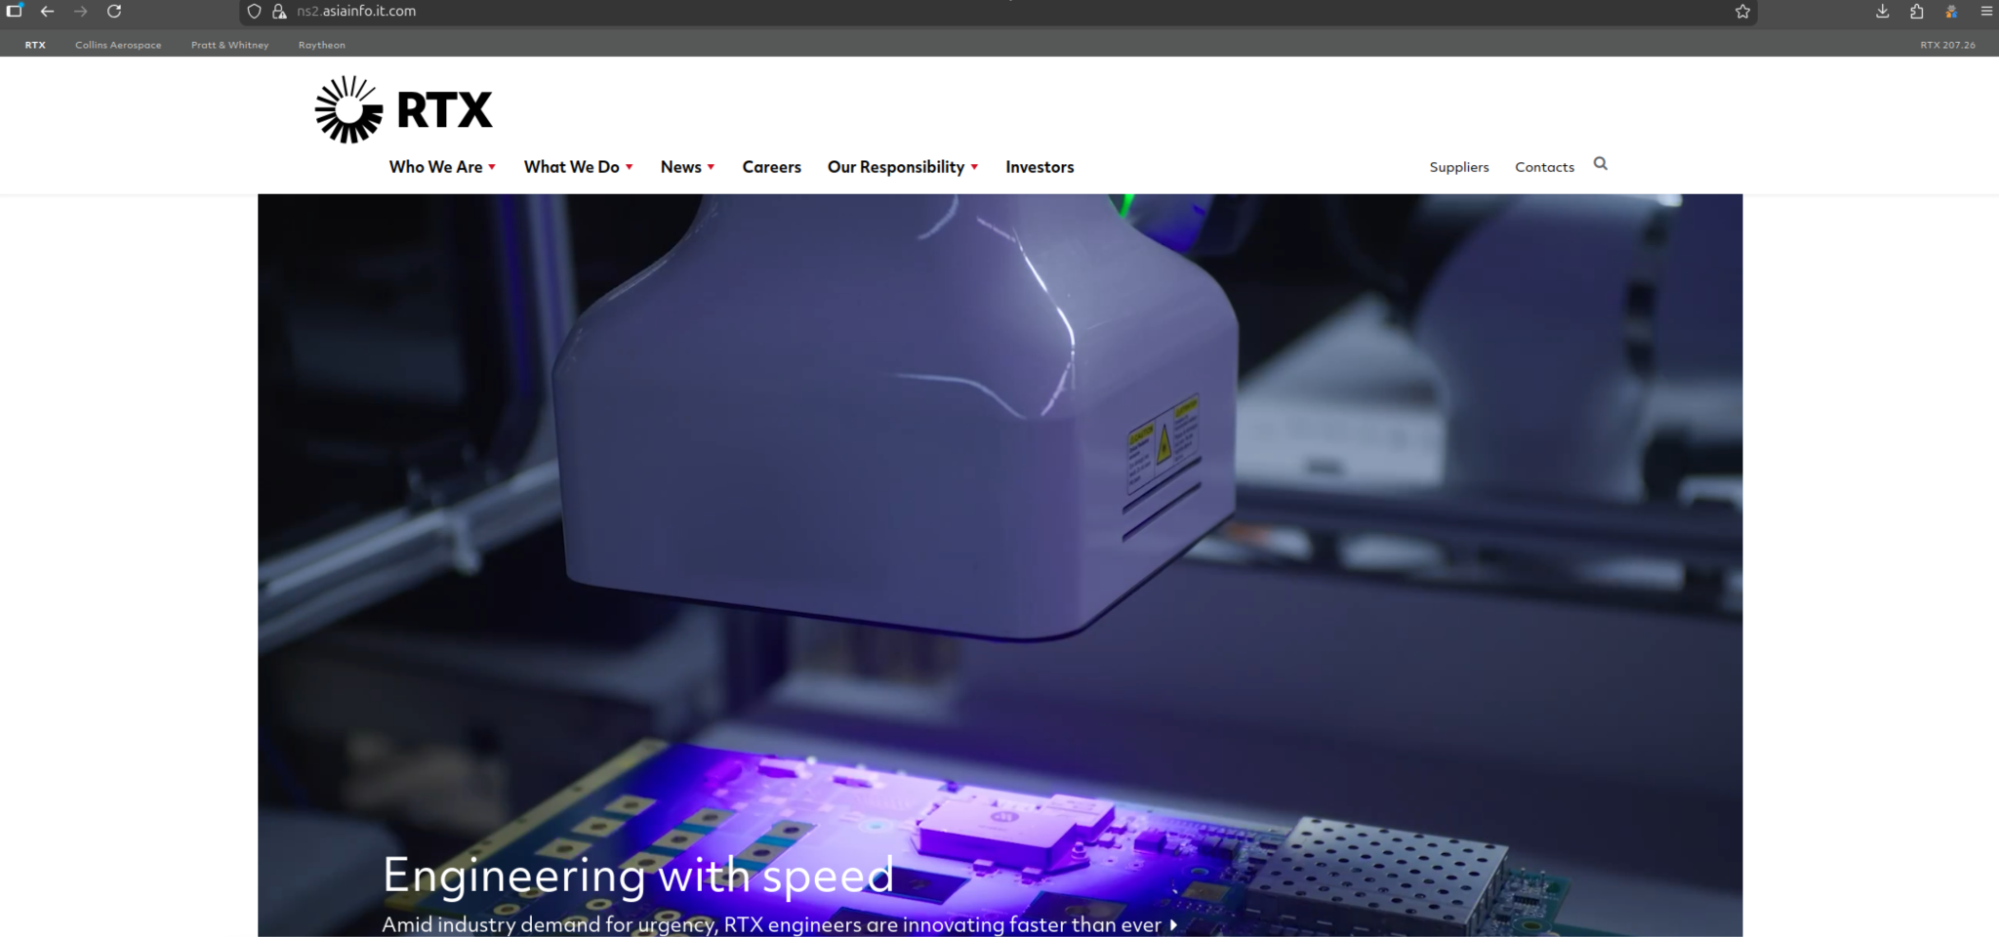 Figure 03: Screenshot of the RTX Corporation impersonation page hosted on ns2.asiainfo.it[.]com
The webpage contained no malicious code, and it is not unique to this server. Why this content was hosted on infrastructure detected as SpiceRAT is explored below.
A Single Cloned Webpage Leads to Thirteen Servers
The RTX corporation homepage is a copy, but not a current one. A review of the page source showed that the stylesheet URLs still carried the build timestamps from when it was scraped, the most recent dated 5 January 2026. Each host that would later serve this webpage came online in the following weeks. The operator(s) captured the site once, and reused it as a template as the infrastructure grew in size.
For defenders, a page reused this way makes for an easy detection signature: byte-for-byte identical wherever it lands, presenting a single hash. After creating a quick HuntSQL query, we identified 13 hosts, and their breakdown and overlaps is the most interesting part.
Query:
SELECT
    *
FROM
    ip.current
WHERE
    html.body.hash.sha256 == "E9D0E8B8A33858A7A5A46F78D7A78F9AA7F9B029348D9B618C6A6A1937A39382"

Copy| IP | Domain | Reseller | AS Name | Country | Last Seen | Status |
|---|---|---|---|---|---|---|
| 185.243.114[.]124 | www[.]tm-mfa.com | CrownCloud | IP-Projects | DE | 2026-07-31 | RTX page only |
| 188.243.115[.]156 | - | CrownCloud | IP-Projects | DE | 2026-08-18 | RTX page only |
| 45.153.125[.]200 | - | - | EDIS GmbH | BG | 2026-08-18 | Bitdefender reported SpiceRAT |
| 194.68.44[.]133 | infrastructure.minings[.]blog | EDIS GmbH | M247 Europe SRL | RO | 2026-08-17 | Bitdefender reported SpiceRAT |
| 2.58.14[.]9188.190.1[.]2085 | azure.uzrailwaystax[.]com | CrownCloud | GWY IT PTY LTD | NL | 2026-08-13 | Hunt.io detected SpiceRAT (2026-08-13) |
| 31.59.185[.]224 | ns.panterstationary[.]online pro.taustas[.]com | - | CGI GLOBAL LIMITED | NL | 2026-08-20 | RTX page only |
| 2.58.15[.]172 | - | CrownCloud | GWY IT PTY LTD | CH | 2026-08-20 | RTX page only |
| 188.190.18[.]208 | www.tmgaz-server[.]com | EDIS GmbH | RJ Network OU | EE | 2026-08-05 | RTX page only |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | NL | 2026-08-27 | RTX page only |
| 31.58.209[.]28 | infoxxe.plan-mail[.]com (Jun-Aug 2026) mail.plan-mail[.]com (Jun-Aug 2026) | CloudBackbone | AS56971 Cloud | NL | 2026-08-20 | RTX page only |
| 45.153.125[.]20 | - | - | EDIS GmbH | BG | 2026-08-17 | Bitdefender reported SpiceRAT |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | - | EDIS GmbH | BG | 2026-08-10 | Hunt.io detected SpiceRAT (Feb 2026) |
| 31.57.92[.]84 | - | CloudBackbone | AS56971 Cloud | LV | 2026-06-10 | RTX page only |
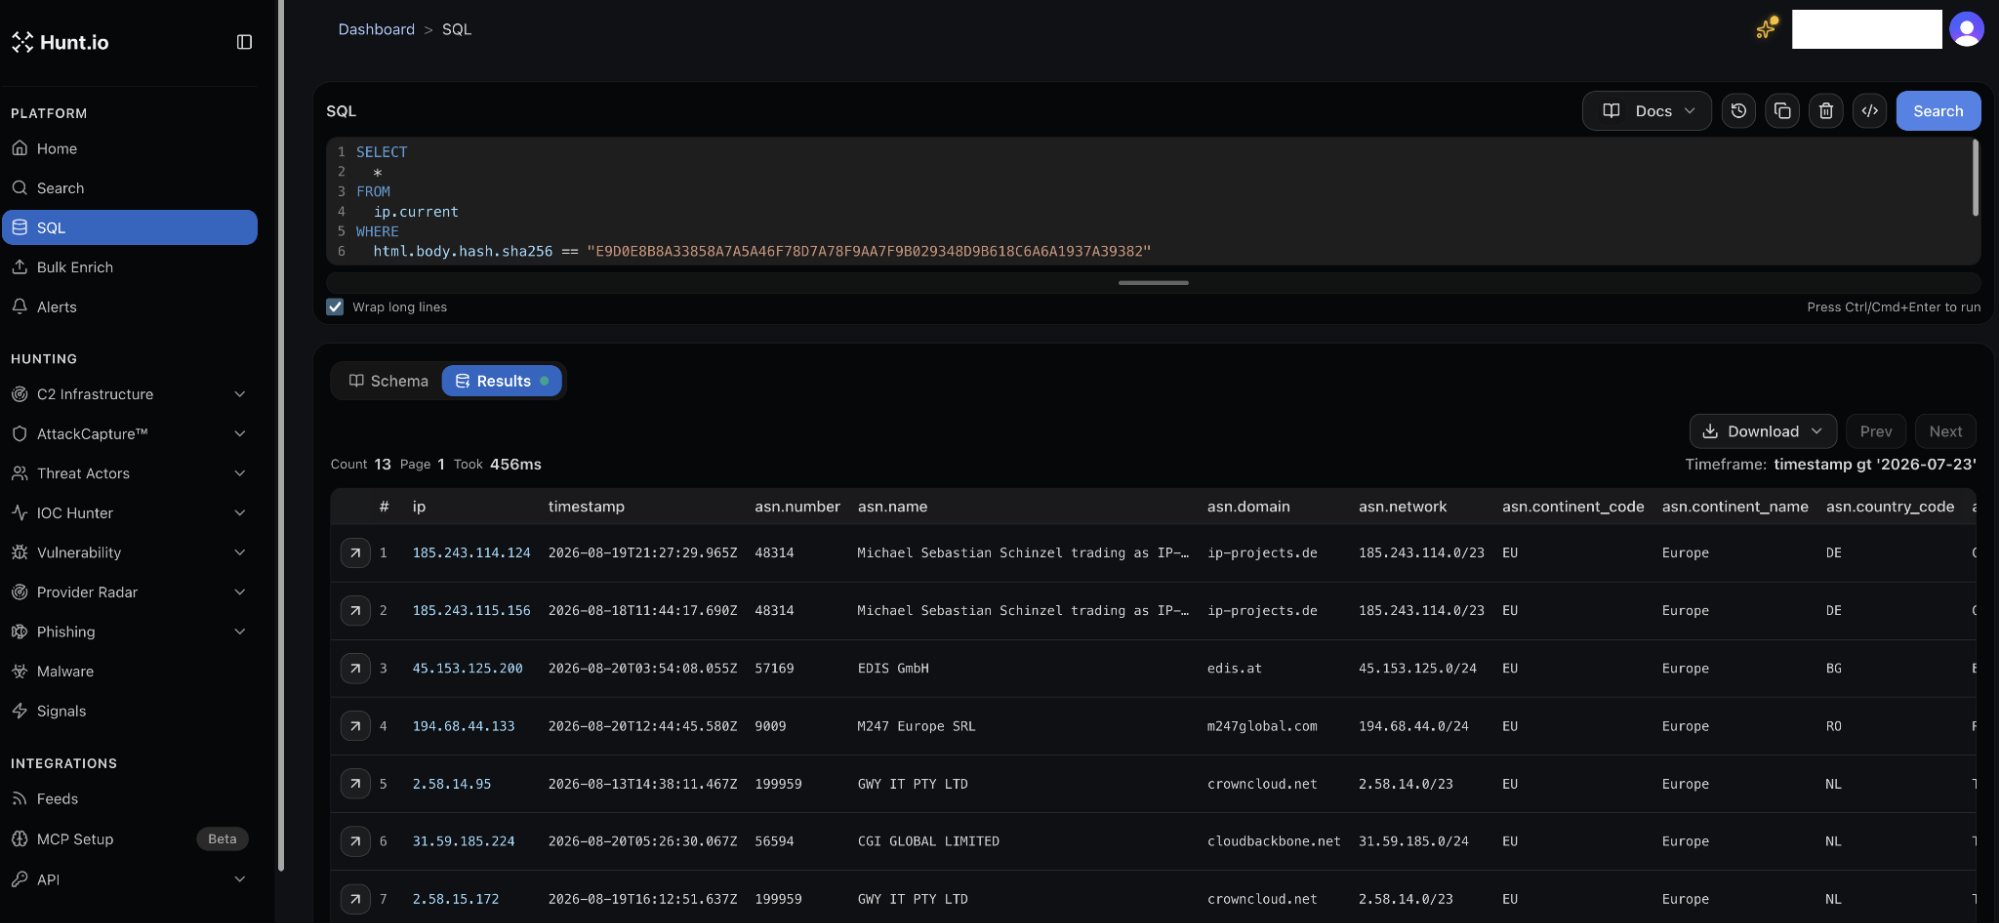 Figure 04: HuntSQL results querying the webpage hash for the copied RTX page.
Three of the 13 appear in the Bitdefender report as SpiceRAT command and control: 45.153.125[.]200, 194.68.44[.]133, and 45.153.125[.]20. Two others, 188.190.29[.]126 and 2.58.14[.]95, also match Hunt.io's SpiceRAT detection signature. The remaining eight are tied by the page, and two specific nginx versions (1.29.3 & 1.31.3) seen across all hosts.
No other host in our dataset has been observed serving this webpage. The ten servers outside the SilkParasite report share artifacts with infrastructure that Bitdefender attributed to SpiceRAT directly, extending the reported footprint of the servers associated with the campaign.
A Static Webpage With Default Content
The cloned page is served on port 80, while SpiceRAT's command channel operates separately on port 443. A review of the RTX source did not reveal any credential forms, payloads, or delivery mechanisms. Two of the five menu sections link to the genuine domain, while the others refresh the page, but modify the URL, indicating this is a likely static, self-contained decoy.
Why RTX was chosen is a separate question that we cannot make a determination at this time. A US defense contractor is an unusual choice to impersonate for infrastructure whose operational domains spoof and target Central Asian ministries and state enterprises. Two explanations are consistent with the evidence: the page was selected arbitrarily because it rendered cleanly, or it originates in shared tooling across operators, where the clone functions as a default deployment asset.
Shared Certificate Artifact on Two Different Providers
On 29 July 2026, 188.190.18[.]208, one of the 13 new IPs, presented a self-signed certificate with the subject and issuer both set to CN=localhost, O=LokiDev. An identical certificate (matched by SHA-256) appeared on 185.243.114[.]238 (AS48314, IP-Projects, Germany) between 28 and 31 July. A HuntSQL query on the organization value confirmed the certificate appeared on these hosts and nowhere else.
185.243.114[.]238 resolved to a single domain, normativ.dushanbeidc[.]org, a NameCheap-registered domain impersonating Tajikistan's national IT-hub project. The domain registrar, hosting provider and country targeting align with the rest of the hosts and the SilkParasite report.
That the same certificate, private key included, appears on two hosts at two providers means both were built from common tooling, and the localhost common name suggests the servers may have been used for testing.
One Certificate, Two Malware Families
TLS certificate hunting on this cluster turned a single SHA-256 match into a link across two malware families.
Of the thirteen RTX hosts, four also presented a TLS certificate on port 443. Its subject is named azure.uzrailwaystax[.]com, a host impersonating Uzbekistan's railway authority. The same certificate, matched by SHA-256, appeared on eight separate hosts total.
| IP | Reseller | AS Name | Country | First Seen (Certificate) | Domains |
|---|---|---|---|---|---|
| 92.243.66[.]71 | - | EDIS GmbH | RU | 16-Jul-26 | - |
| 193.29.56[.]119 | CrownCloud | IP-Projects | DE | 05-Aug-26 | - |
| 2.58.14[.]95 | CrownCloud | GWY IT PTY LTD | NL | 16-Jan-26 | azure.uzrailwaystax[.]com |
| 188.190.18[.]208 | EDIS GmbH | RJ Network OU | EE | 05-Aug-26 | www.tmgaz-server[.]com |
| 171.22.16[.]187 | CrownCloud | IP-Projects | DE | 17-Jul-26 | help.hoster-kg[.]com |
| 193.29.57[.]182 | CrownCloud | IP-Projects | DE | 14-Jul-26 | - |
| 45.153.125[.]20 | - | EDIS GmbH | BG | 31-Jul-26 | - |
| 188.190.29[.]126 | - | EDIS GmbH | BG | 05-Mar-26 | ns2.asiainfo.it[.]com |
Table 2: Hosts presenting the azure.uzrailwaystax[.]com certificate
A simple HuntSQL query was used to unearth the most recent servers hosting the spoofed domain certificate's SHA-256 hash (27E072B92B5AC9E3E2A6770BEF3E84BDF864B0611D3BC9CACA12BE2B1A63DAE4):
Query:
SELECT
  *
FROM
  ip.current
WHERE
  tls.cert.hash.sha256 = '27E072B92B5AC9E3E2A6770BEF3E84BDF864B0611D3BC9CACA12BE2B1A63DAE4'

CopyResult:
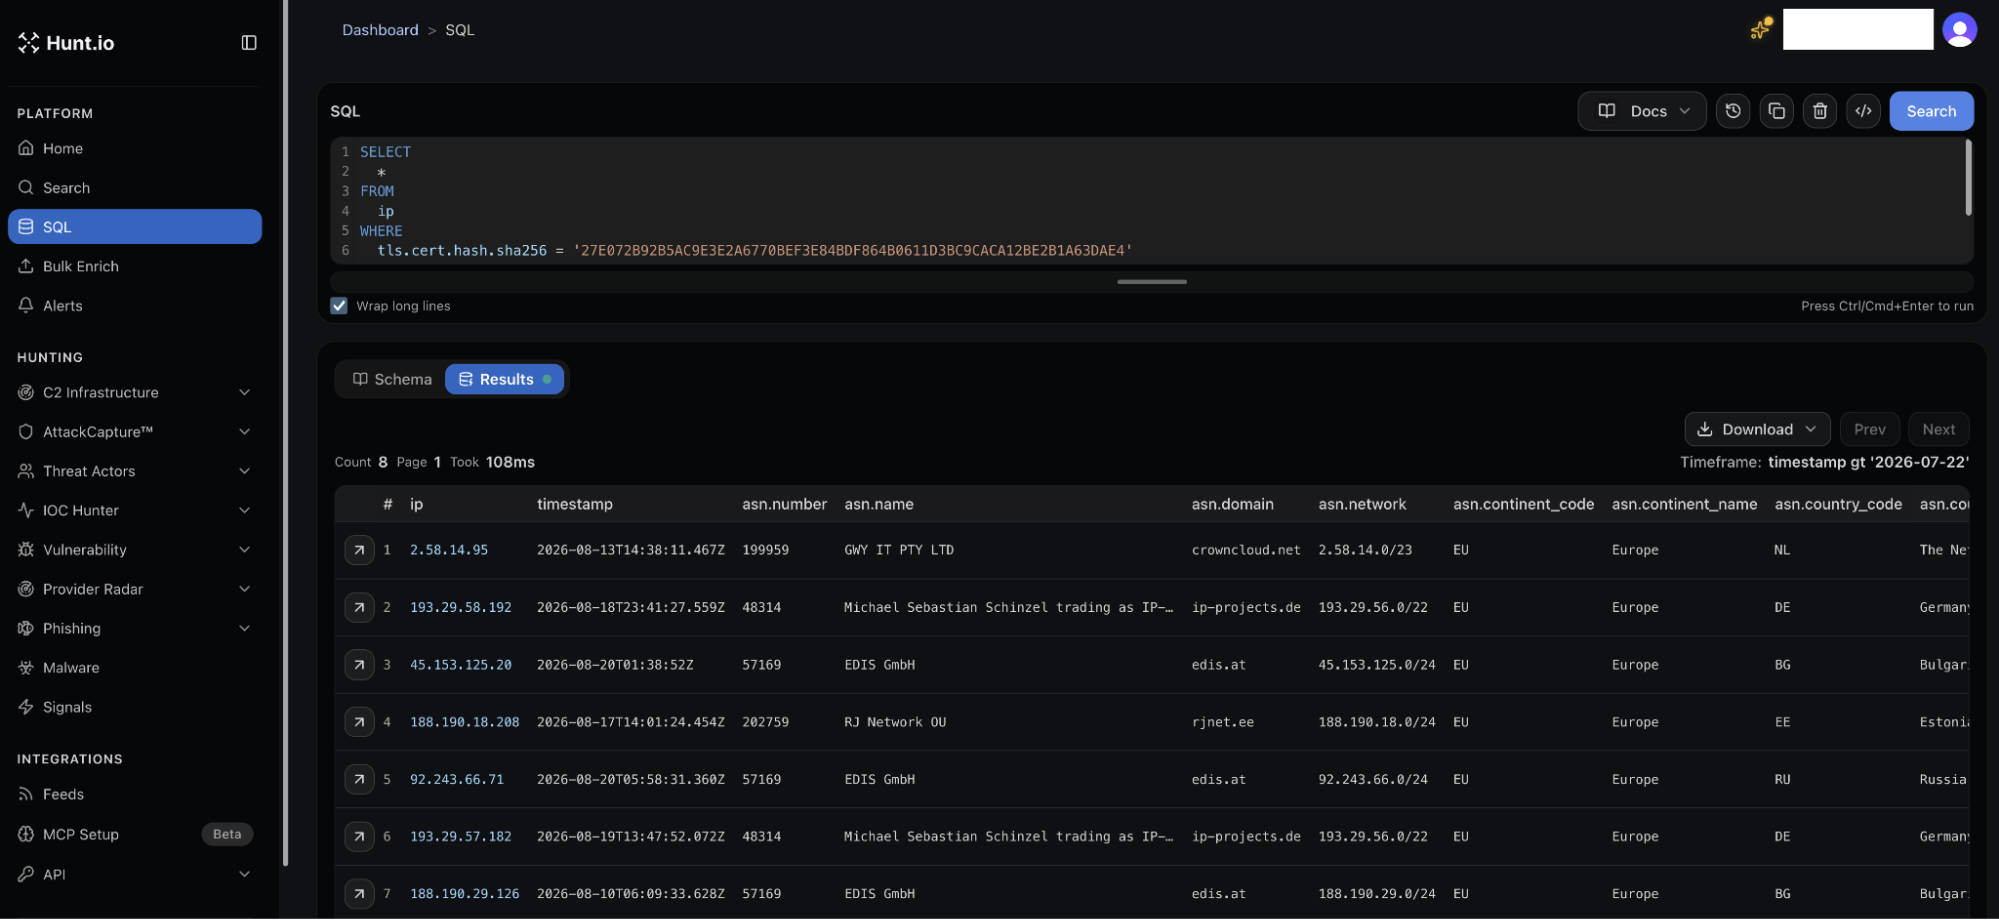 Figure 05: HuntSQL results showing 8 servers identified hosting the azure.uzrailwaystax[.]com certificate SHA-256 fingerprint.
Unlike the cloned webpage, the certificate was not a passive artifact. The certificate was issued on 23 December 2025 and deployed across hosts that came online through the following weeks, a similar window seen in the RTX infrastructure. Four of the eight also carry the RTX page: 45.153.125.20, 188.190.18.208, 188.190.29.126, and 2.58.14.95. Two were independently confirmed as SpiceRAT, one by Bitdefender (.20), and one by Hunt.io (.95).
The Chinese Certificate Authority
The above certificate was issued by TLC DV TLS CA, operated by 泰尔认证中心有限公司 (TL Certification Center, TLC). TLC is wholly funded by the China Academy of Information and Communications Technology (CAICT), a research institute under China's Ministry of Industry and Information Technology.
The issuer is not itself an indicator. A query across our scan data for the past 30 days identified nearly 3,000 servers hosting TLC certificates. A domain-validated certificate impersonating a Central Asian state entity was obtained from a Chinese CA whose public presence is domestic and whose support channels run through a government affiliated institute. The selection of TLC suggests a deliberate one and an operator with access to a China-based procurement channel.
A broader query pairing the certificate's JA4X fingerprint with the TLC issuer field, filtered to the three ASNs most prevalent across the cluster, returned the seven hosts already identified through the SHA-256 match, plus two additional servers.
Query:
SELECT
    *
FROM
    ip.current
WHERE
    tls.cert.hash.ja4x = 'a373a9f83c6b_7022c563de38_4eebb5e6ba4e'
AND
    tls.cert.issuer.common_name = 'TLC DV TLS CA'
AND(
    asn.number = 199959
    OR asn.number = 57169
    OR asn.number = 48314
)

CopyResult:
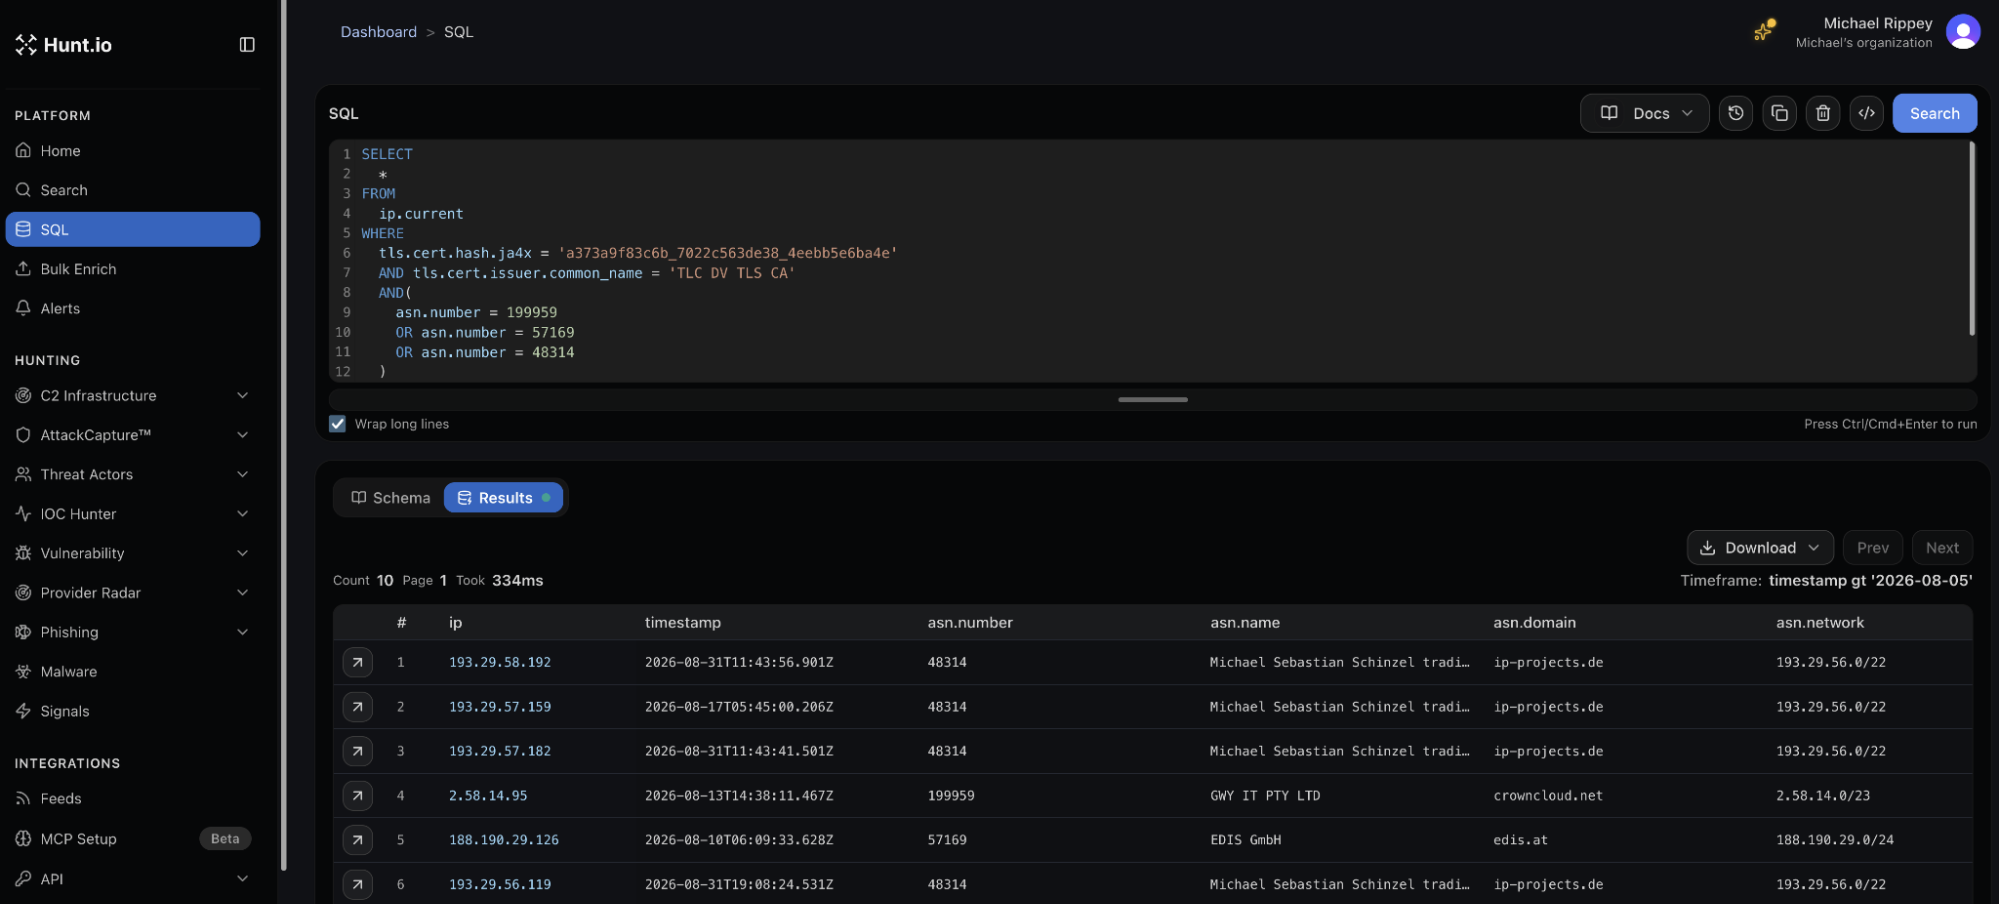 Figure 06: HuntSQL query results showing the hosts presenting the TLC certificate across the three prevalent ASNs.
46.30.189[.]191 (AS199959), hosts a TLC-issued certificate for state.presldent[.]info, a typosquat of the word "president" consistent with the government impersonation seen across this infrastructure cluster. 193.29.57[.]159 presents tmk.natcommunzu[.]com, possibly a spoof of Uzbekistan's national communication sector.
Subdomain enumeration and passive DNS analysis of both domains revealed additional infrastructure on the same providers, with the earliest resolution dating back to mid-2022. A subdomain on natcommunzu[.]com, storage.natcommunzu[.]com, was hosted on 185.243.112[.]253, an Access2.IT server resold through CrownCloud not previously seen in this group of servers, and flagged by Hunt.io's SpiceRAT detection in late 2025. The full subdomain and resolution history is included in the IoC section.
A Registration Link to NodeEdgeRAT
193.29.58[.]192 presents the certificate and resolves to help.hoster-kg[.]com, a domain that DNS history shows moving to this host on 8 January 2026, the same week the earliest SpiceRAT servers came online. Bitdefender attributed a sibling hostname, evo.hoster-kg[.]com, to NodeEdgeRAT. The two families are linked through shared registration of hoster-kg[.]com, not via a shared server.
The domain impersonated in the uzrailwaystax certificate mirrors Bitdefender's published BloodAlchemy C2 domain, uzrailway.devon-uz[.]com. Both spoof the same railway entity. The shared targeting, certificate, and infrastructure suggests a single operator selecting different tools for different tasks, or operators using a different tool on the same parent domain to accomplish a goal.
A Similar Pattern Extends to a Third Malware Family
Several hosts in the cluster expose Remote Desktop on unusually high ports: 64350, 64330, 65535, and 65111. Querying for the above across the cluster's primary ASNs surfaced additional infrastructure matching the previously seen targeting and domain naming pattern.
A note on the protocol filter: modern RDP deployments are typically wrapped in TLS through Network Level Authentication. Scanners fingerprint the exposed service by the outer layer, so hardened RDP appears in scan data under the tls protocol rather than RDP.
The query below reflects that.
SELECT
*
FROM
ip.current
WHERE
same_port(
service.port IN (64350, 64330, 65535, 65111, 61256)
AND
protocol.fingerprint = 'tls' )
AND
asn.number IN (199959, 57169, 48314, 9009)
Copy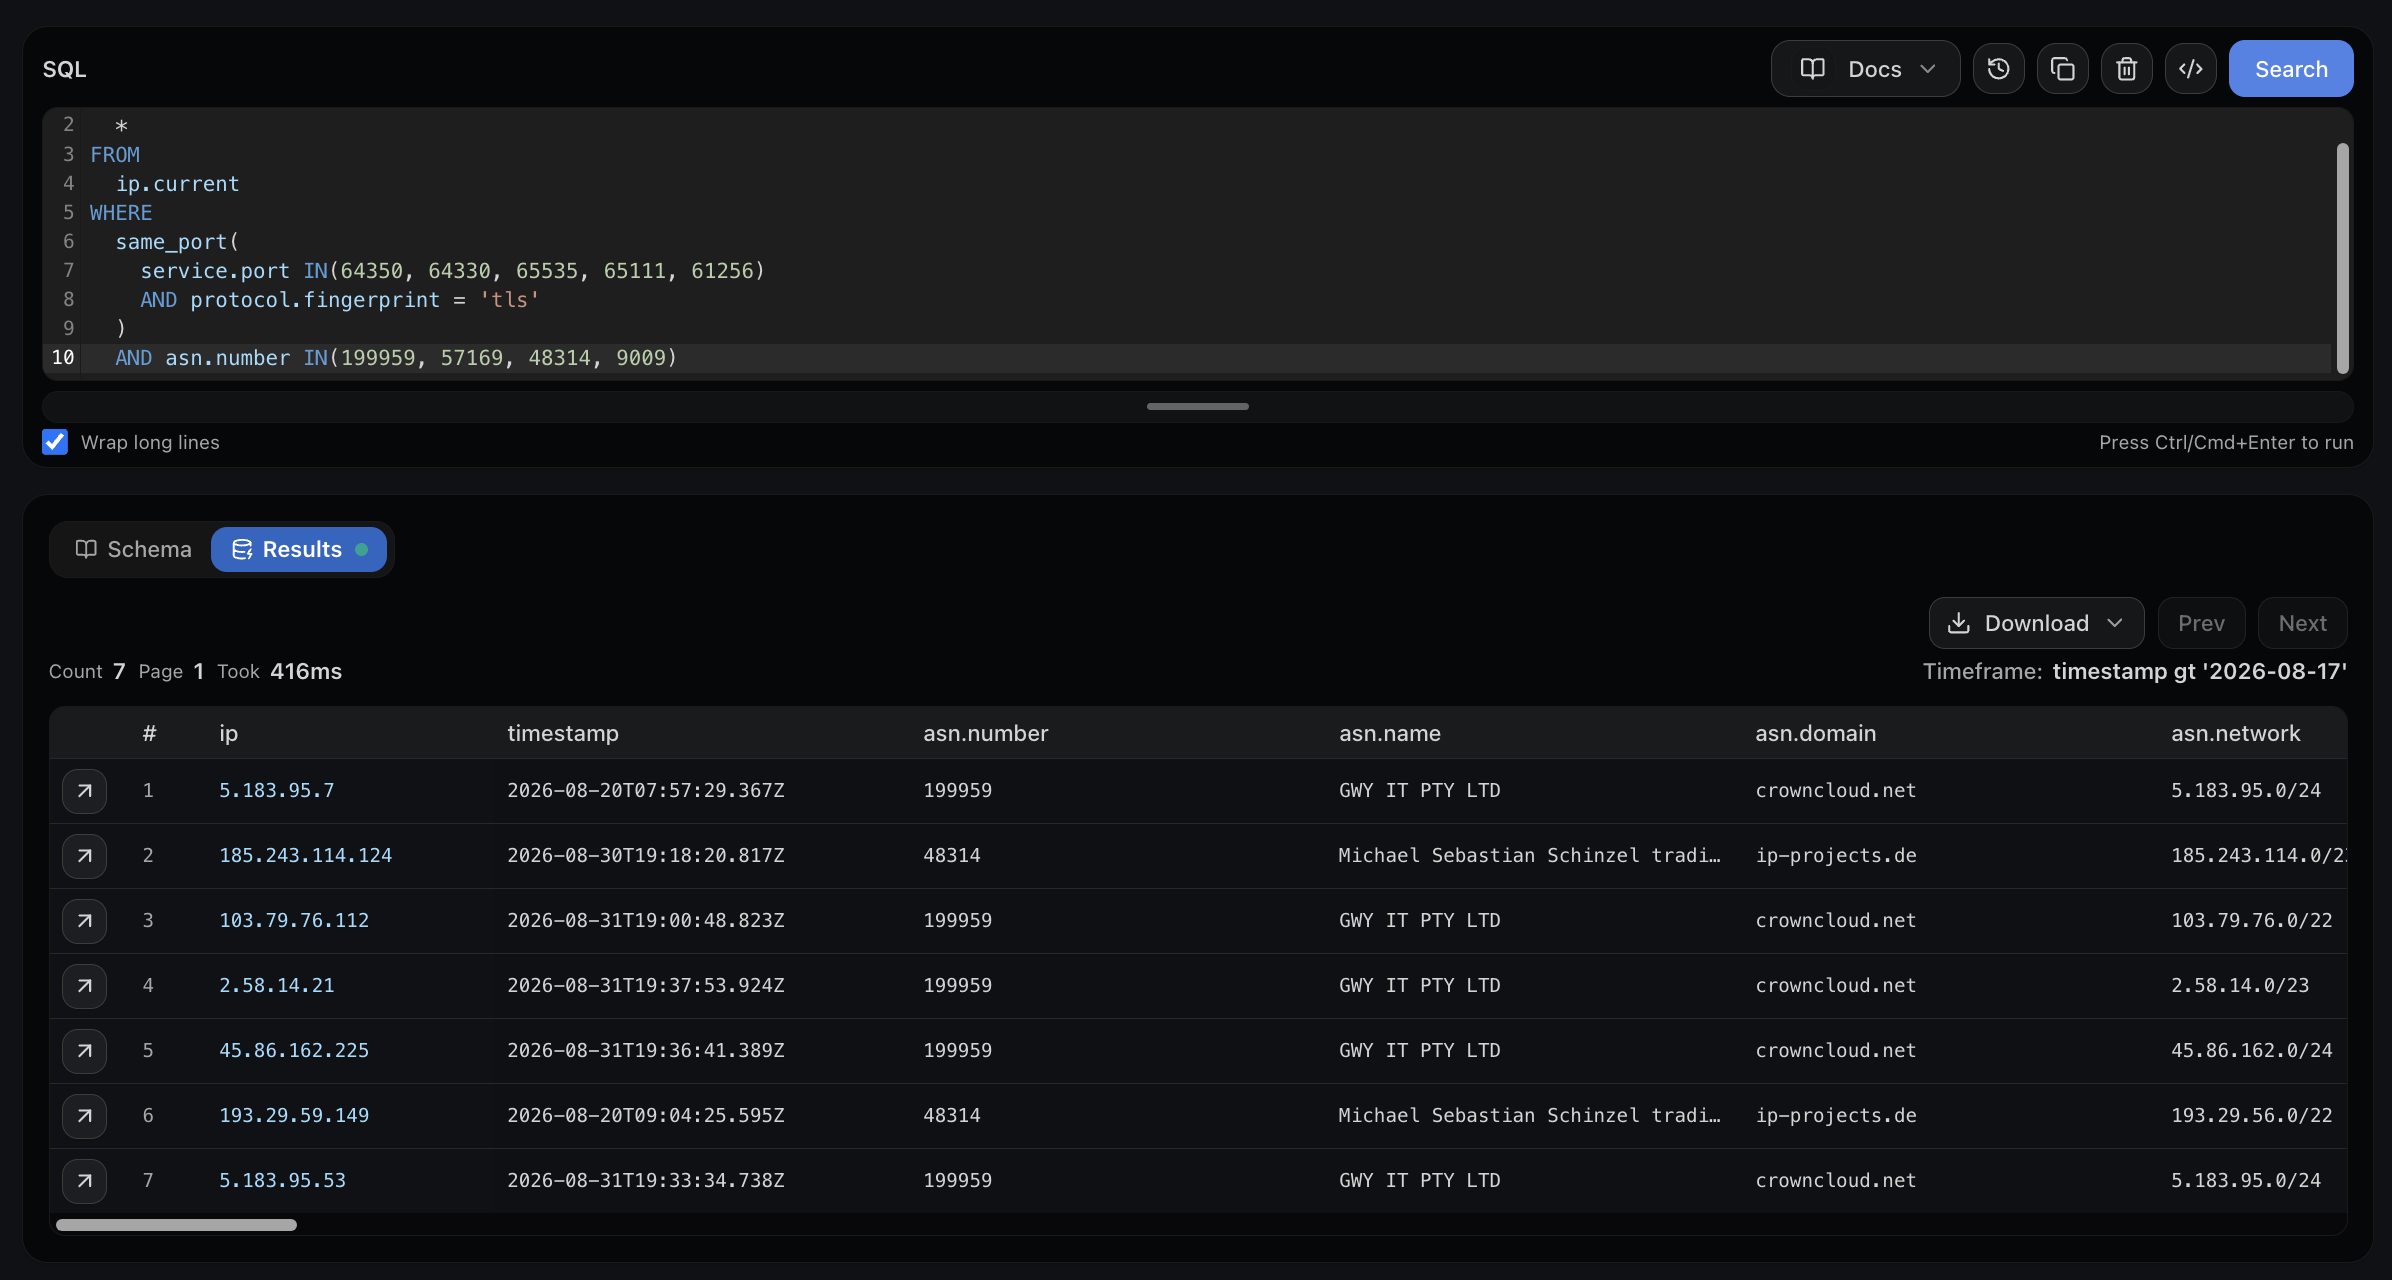 Figure 07: HuntSQL results for the high-numbered ports query, returning 7 hosts running RDP-over-TLS across the cluster's primary ASNs.
Two of the hosts returned carried domains matching the aforementioned patterns. 45.153.127[.]99 resolved to center.infocomkg[.]org and kg.tdtu[.]org. 45.86.162[.]141 resolved to mail.postmfa[.]com. The full result set is included in the Indicators of Compromise section.
kg.tdtu[.]org shares a parent domain with mineconom.tdtu[.]org, published in the SilkParasite report as a NomadRAT C2 indicator. The same registration-level relationship that linked the certificate to NodeEdgeRAT now extends to a third malware family cited in the report.
Targeting Across Central Asia's Government and Energy Sectors
The different hosts across the clusters mentioned above resolve to domains impersonating Central Asian government bodies and state enterprises. Several additional IPs/hostnames surfaced through enrichment of Bitdefender's published indicators, while others were discovered enumerating infrastructure sharing the same hosting profile: CrownCloud and EDIS as resellers on IP-Projects and M247 address space, registered through NameCheap.
The full listing of the IPs and provider mappings can be found in the Indicators of Compromise section.
help.galkynysh[.]net on 91.132.94[.]36 impersonates the Galkynysh gas field in Turkmenistan, one of the world's largest natural gas deposits. The host was reached through enrichment of a Bitdefender-published IP.
tmgaz-server[.]com on 188.190.18[.]208 spoofs Türkmengaz, the state gas company that operates Galkynysh.
tm-mfa[.]com on 185.243.114[.]124 impersonates Turkmenistan's Ministry of Foreign Affairs.
tojiktelecomtj[.]com on 46.30.188[.]54 targets Tojiktelecom, Tajikistan's state telecommunications provider.
gov.mpekz[.]online on 45.153.127[.]186 references a Kazakh government entity.
Additional domains impersonating Turkmen energy (sanly.oilgas-tm[.]com), Uzbekistan government administration (azure.adm-devon[.]com), and the residence of the Kyrgyzstan president (data.yntymak-ordo[.]com) were identified on the same infrastructure profile. Full domain and subdomain enumeration is included in the Indicators of Compromise section.
Bitdefender's targeting picture was derived from recovered lures and infection telemetry. The domains observed during our analysis of the infrastructure identify specific named entities across those same sectors, including Galkynysh, Türkmengaz, Tojiktelecom, and the Turkmenistan Ministry of Foreign Affairs.
Parallels to Previous Central Asia Targeting
The SilkParasite report noted overlaps with FamousSparrow, a suspected China-nexus actor previously documented targeting hotels, government entities, and international organizations. The infrastructure examined here shares additional characteristics with IndigoZebra (also referred to as Speccom by ESET), in a separate cluster reported by Check Point Research in 2021 as targeting Central Asian government ministries and also assessed as suspected China-nexus.
IndigoZebra's infrastructure included kginfocom[.]com and post.mfa-uz[.]com; this cluster includes infocomkg[.]org and mail.postmfa[.]com. Both operators structured subdomains around common service names such as mail, service, and help.
Domain naming patterns and target lists circulate across China-nexus activity through shared tooling, vendor relationships, or independent convention. The overlap is noted here as context alongside the SilkParasite report's FamousSparrow reference.
The full indicator set is provided below.
Indicators of Compromise
Table 1: March 2026 SpiceRAT Cluster
| IP | Hostname | Ports | AS Name | Reseller | Country | First Seen |
|---|---|---|---|---|---|---|
| 46.30.191[.]230 | - | 80, 443 | GWY IT PTY LTD | CrownCloud | NL | 2026-02-09 |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | 80 | EDIS GmbH | - | BG | 2026-02-26 |
| 193.29.59[.]159 | - | 80, 443 | IP-Project | CrownCloud | DE | 2026-03-02 |
| 31.58.220[.]250 | - | 443 | AS56971 Cloud | CloudBackbone | NL | 2026-03-04 |
| 171.22.16[.]187 | ns1.wordcheck[.]info | 443 | Global Connectivity Solutions | - | CH | 2026-03-05 |
Table 2: RTX Page Hash Hosts
| IP | Domain | Reseller | AS Name | Country | Last Seen | Status |
|---|---|---|---|---|---|---|
| 185.243.114[.]124 | www[.]tm-mfa.com | CrownCloud | IP-Projects | DE | 2026-07-31 | RTX page only |
| 185.243.115[.]156 | - | CrownCloud | IP-Projects | DE | 2026-08-18 | RTX page only |
| 45.153.125[.]200 | - | - | EDIS GmbH | BG | 2026-08-18 | Bitdefender reported SpiceRAT |
| 194.68.44[.]133 | infrastructure.minings[.]blog | EDIS GmbH | M247 Europe SRL | RO | 2026-08-17 | Bitdefender reported SpiceRAT |
| 2.58.14[.]95 | azure.uzrailwaystax[.]com | CrownCloud | GWY IT PTY LTD | CH | 2026-08-13 | Hunt.io detected SpiceRAT (2026-08-13) |
| 31.59.185[.]224 | ns.panterstationary[.]online pro.taustas[.]com | - | CGI GLOBAL LIMITED | CH | 2026-08-20 | RTX page only |
| 2.58.15[.]172 | - | CrownCloud | GWY IT PTY LTD | CH | 2026-08-20 | RTX page only |
| 188.190.18[.]208 | www.tmgaz-server[.]com | EDIS GmbH | RJ Network OU | EE | 2026-08-05 | RTX page only |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | CH | 2026-08-27 | RTX page only |
| 31.58.209[.]28 | infoxxe.plan-mail[.]com mail.plan-mail[.]com | CloudBackbone | AS56971 Cloud | CH | 2026-08-20 | RTX page only |
| 45.153.125[.]20 | - | - | EDIS GmbH | BG | 2026-08-17 | Bitdefender reported SpiceRAT |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | - | EDIS GmbH | BG | 2026-08-10 | Hunt.io detected SpiceRAT (Feb 2026) |
| 31.57.92[.]84 | - | CloudBackbone | AS56971 Cloud | LV | 2026-06-10 | RTX page only |
Table 3: azure.uzrailwaystax[.]com Certificate Hosts
| IP | Reseller | Provider | Country | First Seen (Certificate) | Domains |
|---|---|---|---|---|---|
| 92.243.66[.]71 | - | EDIS GmbH | RU | 16-Jul-26 | - |
| 193.29.56[.]119 | CrownCloud | IP-Projects | DE | 05-Aug-26 | - |
| 2.58.14[.]95 | CrownCloud | GWY IT PTY LTD | NL | 16-Jan-26 | azure.uzrailwaystax[.]com |
| 188.190.18[.]208 | EDIS GmbH | RJ Network OU | EE | 05-Aug-26 | www.tmgaz-server[.]com |
| 171.22.16[.]187 | CrownCloud | IP-Projects | DE | 17-Jul-26 | www.wordcheck[.]info ns1.wordcheck[.]info |
| 193.29.57[.]182 | CrownCloud | IP-Projects | DE | 14-Jul-26 | help.hoster-kg[.]com (8-Jan-26 - 4-Sep-26) |
| 45.153.125[.]20 | - | EDIS GmbH | BG | 31-Jul-26 | - |
| 188.190.29[.]126 | - | EDIS GmbH | BG | 05-Mar-26 | ns2.asiainfo.it[.]com |
Table 4: TLS certificate (azure.uzrailwaystax[.]com)
| Field | Value |
|---|---|
| Subject CN | azure.uzrailwaystax[.]com |
| Issuer | TLC DV TLS CA |
| Serial | 81628176171941507003526847276457465393 |
| SHA-1 | 9297D5FD21EF21B16F5880CD4FAEA2AD1FB9EE39 |
| Valid from | 2025-12-23 |
| Valid to | 2026-12-23 |
Table 5: JA4X + Issuer Common Name Certificate Hosts & Subdomain Enumeration
| Domain | IP | AS Name | Reseller | First Seen | Last Seen |
|---|---|---|---|---|---|
| state.presldent[.]info | 46.30.189[.]191 | GWY IT PTY LTD | CrownCloud | 9-Dec-2025 | 4-Sep-2026 |
| cert.presldent[.]info | 46.30.191[.]214 | GWY IT PTY LTD | CrownCloud | 8-Jan-2026 | 4-Sep-2026 |
| check.presldent[.]info | 45.86.163[.]87 | GWY IT PTY LTD | CrownCloud | 8-Jan-2026 | 14-Jan-2026 |
| chief.presldent[.]info | 2.58.15[.]101 | GWY IT PTY LTD | CrownCloud | 22-Nov-2023 | 9-Jul-2024 |
| it.presldent[.]info | 185.253.117[.]32 | HZ Hosting Ltd | - | 7-Aug-2025 | 13-Aug-2025 |
| tmk.natcommunzu[.]com | 193.29.57[.]159 | IP-Projects | CrownCloud | 12-Jan-2026 | 4-Sep-2026 |
| microsoft.natcommunzu[.]com | 46.30.190[.]170 | GWY IT PTY LTD | CrownCloud | 22-Jun-2025 | 4-Sep-2026 |
| storage.natcommunzu[.]com | 185.243.112[.]253 | Access2.IT Group B.V. | CrownCloud | 27-Jul-2022 | 30-Aug-2023 |
| support.natcommunzu[.]com | 185.243.112[.]220 | Access2.IT Group B.V. | CrownCloud | 14-Dec-2023 | 8-Mar-2024 |
| uz.natcommunzu[.]com | 45.67.230[.]185 | UFO Hosting LLC | - | 6-Oct-2023 | 10-Mar-2024 |
Table 6: Additional Servers Impersonating Central Asian Entities
| IP | Domain | Reseller | AS Name | Country |
|---|---|---|---|---|
| 91.132.94[.]36 | help.galkynysh[.]net kg.cwisuz[.]com | EDIS GmbH | Optimus IT d.o.o. | SI |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | NL |
| 45.153.127[.]186 | gov.mpekz[.]online | EDIS GmbH | M247 Europe SRL | US |
| 185.243.114[.]238 | normativ.dushanbeidc[.]org | CrownCloud | IP-Projects | DE |
| 46.30.191[.]232 | normativ.sozandagon[.]org | CrownCloud | GWY IT PTY LTD | NL |
| 192.121.87[.]172 | data.yntymak-ord[.]com | EDIS GmbH | Trabia SRL | MD |
| 193.29.58[.]217 | link.ytnymak-ord[.]com | CrownCloud | IP-Projects | DE |
| 195.88.191[.]70 | center.yntymak-ordo[.]com | CrownCloud | GWY IT PTY LTD | DE |
| 45.153.127[.]38 | azure.adm-devon[.]com | EDIS GmbH | M247 Europe SRL | US |
| 5.183.95[.]49 | uz.adm-devon[.]com | CrownCloud | GWY IT PTY LTD | DE |
| 195.88.191[.]250 | sanly.oilgas-tm[.]com | CrownCloud | GWY IT PTY LTD | DE |
Table 7: High-Numbered Ports Observations & Subdomain Enumeration/Passive DNS
| IP | Port | Domain | Reseller | AS Name | Country | First Seen | Last Seen |
|---|---|---|---|---|---|---|---|
| 45.86.162[.]141 | 65532 | mail.postmfa[.]com | CrownCloud | GWY IT PTY LTD | NL | 9-Jan-2026 | 5-Sep-2026 |
| 45.153.127[.]99 | 65111 | center.infocomkg[.]org kg.tdtu[.]org | EDIS GmbH | M247 Europe SRL | US | 28-Jan-2026 | 5-Sep-2026 |
| 194.14.217[.]199 | - | mail.infocomkg[.]org | EDIS GmbH | M247 Europe SRL | RO | 21-Nov-2025 | 5-Sep-2026 |
| 83.242.96[.]242 | - | service.infocomkg[.]org | - | Individual Entrepreneur Iugov Denis Sergeevich | RU | 12-Apr-2025 | 5-Sep-2026 |
| 185.253.116[.]145 | - | info.tdtu[.]org | - | HZ Hosting Ltd | FR | 23-Jul-2025 | 16-Jan-2026 |
| 193.29.59[.]248 | - | ud.tdtu[.]org | CrownCloud | IP-Projects | DE | 14-Feb-2025 | 23-Jul-2025 |
| 5.183.95[.]7 | 65535 | api.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | DE | 18-Mar-2026 | 5-Sep-2026 |
| 46.30.191[.]90 | - | checkup.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 18-Mar-2026 | 5-Sep-2026 |
| 2.58.15[.]129 | - | help.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 18-Mar-2026 | 5-Sep-2026 |
| 45.86.162[.]249 | - | telecom.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 5-Jun-2026 | 5-Sep-2026 |
Summary
Malware families that Bitdefender's report treated as distinct, SpiceRAT, NodeEdgeRAT, and NomadRAT, share infrastructure at the registration level, pointing to either a single operator managing multiple toolsets or a support function shared across operators. That relationship was visible only from the network side. None of it required access to a compromised host, nor did it rely on malware samples themselves.
The targeting picture that emerges from this infrastructure, named ministries and state enterprises across five Central Asian countries dating back to at least mid-2022 suggests SilkParasite is a more recent label for an operation with much longer and wider footprint. Organizations in the affected sectors and regions can make use of the above indicators and observations to assess their own exposure.
If you're defending energy, government, or telecom infrastructure in the region, book a demo to see how these indicators track in Hunt.io.
Disclosure note: ahead of publishing this research on September 9, 2026, we notified the affected organizations and the relevant national CERTs, sharing a TLP:AMBER advance copy and holding publication to allow review.
The domains and certificates described here are attacker-controlled impersonations, and the affected organizations are named as apparent targets of that impersonation, not as compromised parties. Notification was made where a contact channel was available and does not imply any recipient has reviewed or confirmed these findings.
This research was carried out jointly with researcher Guy Yasur. Together, we tracked a cluster of SpiceRAT command and control servers active from late 2025 through August 2026 across a small subset of European hosting providers. A TLS certificate issued by a Chinese state-affiliated certificate authority associated with the infrastructure impersonates Uzbekistan's state railway authority. Additionally, this cluster also shares registration-level relationships with hosts Bitdefender attributed to three separate malware families in its August 19, 2026 SilkParasite report.
Detection logic built from Cisco Talos' 2024 SpiceRAT research first flagged these servers in late 2025, and in mid-March 2026, we noticed a small group of C2's coming online within days of each other. This analysis relies on internet-wide scan data, and does not address malware behavior, delivery, or initial access.
Key Findings
Shared parent domains and an identical TLS certificate connect this infrastructure to hosts Bitdefender attributed to SpiceRAT, NodeEdgeRAT, and NomadRAT, three of the seven malware families documented in the SilkParasite report.
The certificate imitating the Uzbekistan railway entity was issued by TLC, a certificate authority wholly funded by CAICT, a Chinese state research institute under the Ministry of Industry and Information Technology.
A copy of RTX Corporation's (formerly Raytheon) homepage served as default content on SpiceRAT servers, with the page hash returning only 13 IP's in a HuntSQL query, all exclusive to the cluster.
The impersonation of Uzbekistan railway also appears in Bitdefender's BloodAlchemy C2 domain, and in the certificate observed on Hunt.io's SpiceRAT servers.
Identified domains spoof named entities including Türkmengaz, the Galkynysh gas field, Tojiktelecom, and Turkmenistan's Ministry of Foreign Affairs.
Passive DNS pivots linked to this cluster show subdomain infrastructure dating to at least mid-2022, suggesting this activity has been ongoing for at least four years.
What follows examines each of these findings, beginning with the SpiceRAT servers observed prior to the SilkParasite publication.
SpiceRAT Infrastructure Predating Bitdefender's Report
Hunt.io's C2 Infrastructure module tracks servers matching detection signatures for known malware families, including SpiceRAT. In mid-March 2026, we observed a cluster of five active SpiceRAT servers: 46.30.191[.]230, 188.190.29[.]126, 193.29.59[.]159, 31.58.220[.]250, and 171.22.16[.]187. The five were active together in mid-March 2026, across multiple hosting providers and countries.
Figure 01: Historical screenshot showing a cluster of five (after deduplication) SpiceRAT servers observed in March 2026.C2 detections establish what is running on a particular server, not who may be operating it. Grouping these hosts required a commonality, and the servers examined throughout this post are linked by at least one of three artifacts: a hostname, TLS certificate, or an identical page hash. These shared characteristics are stronger evidence of a shared operation than a shared malware family. Autonomous System (AS) names and reseller brands diverge across much of the infrastructure described in this analysis. The hosting section visited later addresses that in detail.
Hostname Reuse Across Reported and Unreported Servers
ns2.asiainfo.it[.]com resolved to three SpiceRAT servers in three different countries: 185.122.185[.]36 in Estonia on 24 January 2026, 194.71.107[.]243 in Bulgaria on 30 January, and 188.190.29[.]126 on 26 February, and where it currently resolves as of this post's publication. Each IP is hosted on a separate hosting provider network.
The Bitdefender report lists manager.skycom[.]support among its SpiceRAT indicators. The same hostname resolves to two servers absent from BitDefender's IoC list: 194.68.225[.]168 and 194.14.217[.]119, both detected in late January 2026, exposing ports 80 and 443. As of this post's publication, the domain no longer resolves to either server. Four servers published in the SilkParasite research were already flagged by Hunt.io, with the earliest dating to 2025.
Figure 02: 185.122.185.36 IP intelligence data showing a SpiceRat detection on port 80RTX Corporation Homepage Hosted on SpiceRAT Infrastructure
Requests to ns2.asiainfo.it[.]com on 188.190.29[.]126 returned a complete copy of RTX Corporation's homepage, including navigation, subsidiary links, and a stock ticker.
Figure 03: Screenshot of the RTX Corporation impersonation page hosted on ns2.asiainfo.it[.]comThe webpage contained no malicious code, and it is not unique to this server. Why this content was hosted on infrastructure detected as SpiceRAT is explored below.
A Single Cloned Webpage Leads to Thirteen Servers
The RTX corporation homepage is a copy, but not a current one. A review of the page source showed that the stylesheet URLs still carried the build timestamps from when it was scraped, the most recent dated 5 January 2026. Each host that would later serve this webpage came online in the following weeks. The operator(s) captured the site once, and reused it as a template as the infrastructure grew in size.
For defenders, a page reused this way makes for an easy detection signature: byte-for-byte identical wherever it lands, presenting a single hash. After creating a quick HuntSQL query, we identified 13 hosts, and their breakdown and overlaps is the most interesting part.
Query:
SELECT
    *
FROM
    ip.current
WHERE
    html.body.hash.sha256 == "E9D0E8B8A33858A7A5A46F78D7A78F9AA7F9B029348D9B618C6A6A1937A39382"

Copy| IP | Domain | Reseller | AS Name | Country | Last Seen | Status |
|---|---|---|---|---|---|---|
| 185.243.114[.]124 | www[.]tm-mfa.com | CrownCloud | IP-Projects | DE | 2026-07-31 | RTX page only |
| 188.243.115[.]156 | - | CrownCloud | IP-Projects | DE | 2026-08-18 | RTX page only |
| 45.153.125[.]200 | - | - | EDIS GmbH | BG | 2026-08-18 | Bitdefender reported SpiceRAT |
| 194.68.44[.]133 | infrastructure.minings[.]blog | EDIS GmbH | M247 Europe SRL | RO | 2026-08-17 | Bitdefender reported SpiceRAT |
| 2.58.14[.]9188.190.1[.]2085 | azure.uzrailwaystax[.]com | CrownCloud | GWY IT PTY LTD | NL | 2026-08-13 | Hunt.io detected SpiceRAT (2026-08-13) |
| 31.59.185[.]224 | ns.panterstationary[.]online pro.taustas[.]com | - | CGI GLOBAL LIMITED | NL | 2026-08-20 | RTX page only |
| 2.58.15[.]172 | - | CrownCloud | GWY IT PTY LTD | CH | 2026-08-20 | RTX page only |
| 188.190.18[.]208 | www.tmgaz-server[.]com | EDIS GmbH | RJ Network OU | EE | 2026-08-05 | RTX page only |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | NL | 2026-08-27 | RTX page only |
| 31.58.209[.]28 | infoxxe.plan-mail[.]com (Jun-Aug 2026) mail.plan-mail[.]com (Jun-Aug 2026) | CloudBackbone | AS56971 Cloud | NL | 2026-08-20 | RTX page only |
| 45.153.125[.]20 | - | - | EDIS GmbH | BG | 2026-08-17 | Bitdefender reported SpiceRAT |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | - | EDIS GmbH | BG | 2026-08-10 | Hunt.io detected SpiceRAT (Feb 2026) |
| 31.57.92[.]84 | - | CloudBackbone | AS56971 Cloud | LV | 2026-06-10 | RTX page only |
Figure 04: HuntSQL results querying the webpage hash for the copied RTX page.Three of the 13 appear in the Bitdefender report as SpiceRAT command and control: 45.153.125[.]200, 194.68.44[.]133, and 45.153.125[.]20. Two others, 188.190.29[.]126 and 2.58.14[.]95, also match Hunt.io's SpiceRAT detection signature. The remaining eight are tied by the page, and two specific nginx versions (1.29.3 & 1.31.3) seen across all hosts.
No other host in our dataset has been observed serving this webpage. The ten servers outside the SilkParasite report share artifacts with infrastructure that Bitdefender attributed to SpiceRAT directly, extending the reported footprint of the servers associated with the campaign.
A Static Webpage With Default Content
The cloned page is served on port 80, while SpiceRAT's command channel operates separately on port 443. A review of the RTX source did not reveal any credential forms, payloads, or delivery mechanisms. Two of the five menu sections link to the genuine domain, while the others refresh the page, but modify the URL, indicating this is a likely static, self-contained decoy.
Why RTX was chosen is a separate question that we cannot make a determination at this time. A US defense contractor is an unusual choice to impersonate for infrastructure whose operational domains spoof and target Central Asian ministries and state enterprises. Two explanations are consistent with the evidence: the page was selected arbitrarily because it rendered cleanly, or it originates in shared tooling across operators, where the clone functions as a default deployment asset.
Shared Certificate Artifact on Two Different Providers
On 29 July 2026, 188.190.18[.]208, one of the 13 new IPs, presented a self-signed certificate with the subject and issuer both set to CN=localhost, O=LokiDev. An identical certificate (matched by SHA-256) appeared on 185.243.114[.]238 (AS48314, IP-Projects, Germany) between 28 and 31 July. A HuntSQL query on the organization value confirmed the certificate appeared on these hosts and nowhere else.
185.243.114[.]238 resolved to a single domain, normativ.dushanbeidc[.]org, a NameCheap-registered domain impersonating Tajikistan's national IT-hub project. The domain registrar, hosting provider and country targeting align with the rest of the hosts and the SilkParasite report.
That the same certificate, private key included, appears on two hosts at two providers means both were built from common tooling, and the localhost common name suggests the servers may have been used for testing.
One Certificate, Two Malware Families
TLS certificate hunting on this cluster turned a single SHA-256 match into a link across two malware families.
Of the thirteen RTX hosts, four also presented a TLS certificate on port 443. Its subject is named azure.uzrailwaystax[.]com, a host impersonating Uzbekistan's railway authority. The same certificate, matched by SHA-256, appeared on eight separate hosts total.
| IP | Reseller | AS Name | Country | First Seen (Certificate) | Domains |
|---|---|---|---|---|---|
| 92.243.66[.]71 | - | EDIS GmbH | RU | 16-Jul-26 | - |
| 193.29.56[.]119 | CrownCloud | IP-Projects | DE | 05-Aug-26 | - |
| 2.58.14[.]95 | CrownCloud | GWY IT PTY LTD | NL | 16-Jan-26 | azure.uzrailwaystax[.]com |
| 188.190.18[.]208 | EDIS GmbH | RJ Network OU | EE | 05-Aug-26 | www.tmgaz-server[.]com |
| 171.22.16[.]187 | CrownCloud | IP-Projects | DE | 17-Jul-26 | help.hoster-kg[.]com |
| 193.29.57[.]182 | CrownCloud | IP-Projects | DE | 14-Jul-26 | - |
| 45.153.125[.]20 | - | EDIS GmbH | BG | 31-Jul-26 | - |
| 188.190.29[.]126 | - | EDIS GmbH | BG | 05-Mar-26 | ns2.asiainfo.it[.]com |
Table 2: Hosts presenting the azure.uzrailwaystax[.]com certificate
A simple HuntSQL query was used to unearth the most recent servers hosting the spoofed domain certificate's SHA-256 hash (27E072B92B5AC9E3E2A6770BEF3E84BDF864B0611D3BC9CACA12BE2B1A63DAE4):
Query:
SELECT
  *
FROM
  ip.current
WHERE
  tls.cert.hash.sha256 = '27E072B92B5AC9E3E2A6770BEF3E84BDF864B0611D3BC9CACA12BE2B1A63DAE4'

CopyResult:
Figure 05: HuntSQL results showing 8 servers identified hosting the azure.uzrailwaystax[.]com certificate SHA-256 fingerprint.Unlike the cloned webpage, the certificate was not a passive artifact. The certificate was issued on 23 December 2025 and deployed across hosts that came online through the following weeks, a similar window seen in the RTX infrastructure. Four of the eight also carry the RTX page: 45.153.125.20, 188.190.18.208, 188.190.29.126, and 2.58.14.95. Two were independently confirmed as SpiceRAT, one by Bitdefender (.20), and one by Hunt.io (.95).
The Chinese Certificate Authority
The above certificate was issued by TLC DV TLS CA, operated by 泰尔认证中心有限公司 (TL Certification Center, TLC). TLC is wholly funded by the China Academy of Information and Communications Technology (CAICT), a research institute under China's Ministry of Industry and Information Technology.
The issuer is not itself an indicator. A query across our scan data for the past 30 days identified nearly 3,000 servers hosting TLC certificates. A domain-validated certificate impersonating a Central Asian state entity was obtained from a Chinese CA whose public presence is domestic and whose support channels run through a government affiliated institute. The selection of TLC suggests a deliberate one and an operator with access to a China-based procurement channel.
A broader query pairing the certificate's JA4X fingerprint with the TLC issuer field, filtered to the three ASNs most prevalent across the cluster, returned the seven hosts already identified through the SHA-256 match, plus two additional servers.
Query:
SELECT
    *
FROM
    ip.current
WHERE
    tls.cert.hash.ja4x = 'a373a9f83c6b_7022c563de38_4eebb5e6ba4e'
AND
    tls.cert.issuer.common_name = 'TLC DV TLS CA'
AND(
    asn.number = 199959
    OR asn.number = 57169
    OR asn.number = 48314
)

CopyResult:
Figure 06: HuntSQL query results showing the hosts presenting the TLC certificate across the three prevalent ASNs.46.30.189[.]191 (AS199959), hosts a TLC-issued certificate for state.presldent[.]info, a typosquat of the word "president" consistent with the government impersonation seen across this infrastructure cluster. 193.29.57[.]159 presents tmk.natcommunzu[.]com, possibly a spoof of Uzbekistan's national communication sector.
Subdomain enumeration and passive DNS analysis of both domains revealed additional infrastructure on the same providers, with the earliest resolution dating back to mid-2022. A subdomain on natcommunzu[.]com, storage.natcommunzu[.]com, was hosted on 185.243.112[.]253, an Access2.IT server resold through CrownCloud not previously seen in this group of servers, and flagged by Hunt.io's SpiceRAT detection in late 2025. The full subdomain and resolution history is included in the IoC section.
A Registration Link to NodeEdgeRAT
193.29.58[.]192 presents the certificate and resolves to help.hoster-kg[.]com, a domain that DNS history shows moving to this host on 8 January 2026, the same week the earliest SpiceRAT servers came online. Bitdefender attributed a sibling hostname, evo.hoster-kg[.]com, to NodeEdgeRAT. The two families are linked through shared registration of hoster-kg[.]com, not via a shared server.
The domain impersonated in the uzrailwaystax certificate mirrors Bitdefender's published BloodAlchemy C2 domain, uzrailway.devon-uz[.]com. Both spoof the same railway entity. The shared targeting, certificate, and infrastructure suggests a single operator selecting different tools for different tasks, or operators using a different tool on the same parent domain to accomplish a goal.
A Similar Pattern Extends to a Third Malware Family
Several hosts in the cluster expose Remote Desktop on unusually high ports: 64350, 64330, 65535, and 65111. Querying for the above across the cluster's primary ASNs surfaced additional infrastructure matching the previously seen targeting and domain naming pattern.
A note on the protocol filter: modern RDP deployments are typically wrapped in TLS through Network Level Authentication. Scanners fingerprint the exposed service by the outer layer, so hardened RDP appears in scan data under the tls protocol rather than RDP.
The query below reflects that.
SELECT
 *
FROM
 ip.current
WHERE
 same_port(
   service.port IN (64350, 64330, 65535, 65111, 61256)
AND
 protocol.fingerprint = 'tls' )
AND
 asn.number IN (199959, 57169, 48314, 9009)

CopyTwo of the hosts returned carried domains matching the aforementioned patterns. 45.153.127[.]99 resolved to center.infocomkg[.]org and kg.tdtu[.]org. 45.86.162[.]141 resolved to mail.postmfa[.]com. The full result set is included in the Indicators of Compromise section.
kg.tdtu[.]org shares a parent domain with mineconom.tdtu[.]org, published in the SilkParasite report as a NomadRAT C2 indicator. The same registration-level relationship that linked the certificate to NodeEdgeRAT now extends to a third malware family cited in the report.
Targeting Across Central Asia's Government and Energy Sectors
The different hosts across the clusters mentioned above resolve to domains impersonating Central Asian government bodies and state enterprises. Several additional IPs/hostnames surfaced through enrichment of Bitdefender's published indicators, while others were discovered enumerating infrastructure sharing the same hosting profile: CrownCloud and EDIS as resellers on IP-Projects and M247 address space, registered through NameCheap.
The full listing of the IPs and provider mappings can be found in the Indicators of Compromise section.
help.galkynysh[.]net on 91.132.94[.]36 impersonates the Galkynysh gas field in Turkmenistan, one of the world's largest natural gas deposits. The host was reached through enrichment of a Bitdefender-published IP.
tmgaz-server[.]com on 188.190.18[.]208 spoofs Türkmengaz, the state gas company that operates Galkynysh.
tm-mfa[.]com on 185.243.114[.]124 impersonates Turkmenistan's Ministry of Foreign Affairs.
tojiktelecomtj[.]com on 46.30.188[.]54 targets Tojiktelecom, Tajikistan's state telecommunications provider.
gov.mpekz[.]online on 45.153.127[.]186 references a Kazakh government entity.
Additional domains impersonating Turkmen energy (sanly.oilgas-tm[.]com), Uzbekistan government administration (azure.adm-devon[.]com), and the residence of the Kyrgyzstan president (data.yntymak-ordo[.]com) were identified on the same infrastructure profile. Full domain and subdomain enumeration is included in the Indicators of Compromise section.
Bitdefender's targeting picture was derived from recovered lures and infection telemetry. The domains observed during our analysis of the infrastructure identify specific named entities across those same sectors, including Galkynysh, Türkmengaz, Tojiktelecom, and the Turkmenistan Ministry of Foreign Affairs.
Parallels to Previous Central Asia Targeting
The SilkParasite report noted overlaps with FamousSparrow, a suspected China-nexus actor previously documented targeting hotels, government entities, and international organizations. The infrastructure examined here shares additional characteristics with IndigoZebra (also referred to as Speccom by ESET), in a separate cluster reported by Check Point Research in 2021 as targeting Central Asian government ministries and also assessed as suspected China-nexus.
IndigoZebra's infrastructure included kginfocom[.]com and post.mfa-uz[.]com; this cluster includes infocomkg[.]org and mail.postmfa[.]com. Both operators structured subdomains around common service names such as mail, service, and help.
Domain naming patterns and target lists circulate across China-nexus activity through shared tooling, vendor relationships, or independent convention. The overlap is noted here as context alongside the SilkParasite report's FamousSparrow reference.
The full indicator set is provided below.
Indicators of Compromise
Table 1: March 2026 SpiceRAT Cluster
| IP | Hostname | Ports | AS Name | Reseller | Country | First Seen |
|---|---|---|---|---|---|---|
| 46.30.191[.]230 | - | 80, 443 | GWY IT PTY LTD | CrownCloud | NL | 2026-02-09 |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | 80 | EDIS GmbH | - | BG | 2026-02-26 |
| 193.29.59[.]159 | - | 80, 443 | IP-Project | CrownCloud | DE | 2026-03-02 |
| 31.58.220[.]250 | - | 443 | AS56971 Cloud | CloudBackbone | NL | 2026-03-04 |
| 171.22.16[.]187 | ns1.wordcheck[.]info | 443 | Global Connectivity Solutions | - | CH | 2026-03-05 |
Table 2: RTX Page Hash Hosts
| IP | Domain | Reseller | AS Name | Country | Last Seen | Status |
|---|---|---|---|---|---|---|
| 185.243.114[.]124 | www[.]tm-mfa.com | CrownCloud | IP-Projects | DE | 2026-07-31 | RTX page only |
| 185.243.115[.]156 | - | CrownCloud | IP-Projects | DE | 2026-08-18 | RTX page only |
| 45.153.125[.]200 | - | - | EDIS GmbH | BG | 2026-08-18 | Bitdefender reported SpiceRAT |
| 194.68.44[.]133 | infrastructure.minings[.]blog | EDIS GmbH | M247 Europe SRL | RO | 2026-08-17 | Bitdefender reported SpiceRAT |
| 2.58.14[.]95 | azure.uzrailwaystax[.]com | CrownCloud | GWY IT PTY LTD | CH | 2026-08-13 | Hunt.io detected SpiceRAT (2026-08-13) |
| 31.59.185[.]224 | ns.panterstationary[.]online pro.taustas[.]com | - | CGI GLOBAL LIMITED | CH | 2026-08-20 | RTX page only |
| 2.58.15[.]172 | - | CrownCloud | GWY IT PTY LTD | CH | 2026-08-20 | RTX page only |
| 188.190.18[.]208 | www.tmgaz-server[.]com | EDIS GmbH | RJ Network OU | EE | 2026-08-05 | RTX page only |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | CH | 2026-08-27 | RTX page only |
| 31.58.209[.]28 | infoxxe.plan-mail[.]com mail.plan-mail[.]com | CloudBackbone | AS56971 Cloud | CH | 2026-08-20 | RTX page only |
| 45.153.125[.]20 | - | - | EDIS GmbH | BG | 2026-08-17 | Bitdefender reported SpiceRAT |
| 188.190.29[.]126 | ns2.asiainfo.it[.]com | - | EDIS GmbH | BG | 2026-08-10 | Hunt.io detected SpiceRAT (Feb 2026) |
| 31.57.92[.]84 | - | CloudBackbone | AS56971 Cloud | LV | 2026-06-10 | RTX page only |
Table 3: azure.uzrailwaystax[.]com Certificate Hosts
| IP | Reseller | Provider | Country | First Seen (Certificate) | Domains |
|---|---|---|---|---|---|
| 92.243.66[.]71 | - | EDIS GmbH | RU | 16-Jul-26 | - |
| 193.29.56[.]119 | CrownCloud | IP-Projects | DE | 05-Aug-26 | - |
| 2.58.14[.]95 | CrownCloud | GWY IT PTY LTD | NL | 16-Jan-26 | azure.uzrailwaystax[.]com |
| 188.190.18[.]208 | EDIS GmbH | RJ Network OU | EE | 05-Aug-26 | www.tmgaz-server[.]com |
| 171.22.16[.]187 | CrownCloud | IP-Projects | DE | 17-Jul-26 | www.wordcheck[.]info ns1.wordcheck[.]info |
| 193.29.57[.]182 | CrownCloud | IP-Projects | DE | 14-Jul-26 | help.hoster-kg[.]com (8-Jan-26 - 4-Sep-26) |
| 45.153.125[.]20 | - | EDIS GmbH | BG | 31-Jul-26 | - |
| 188.190.29[.]126 | - | EDIS GmbH | BG | 05-Mar-26 | ns2.asiainfo.it[.]com |
Table 4: TLS certificate (azure.uzrailwaystax[.]com)
| Field | Value |
|---|---|
| Subject CN | azure.uzrailwaystax[.]com |
| Issuer | TLC DV TLS CA |
| Serial | 81628176171941507003526847276457465393 |
| SHA-1 | 9297D5FD21EF21B16F5880CD4FAEA2AD1FB9EE39 |
| Valid from | 2025-12-23 |
| Valid to | 2026-12-23 |
Table 5: JA4X + Issuer Common Name Certificate Hosts & Subdomain Enumeration
| Domain | IP | AS Name | Reseller | First Seen | Last Seen |
|---|---|---|---|---|---|
| state.presldent[.]info | 46.30.189[.]191 | GWY IT PTY LTD | CrownCloud | 9-Dec-2025 | 4-Sep-2026 |
| cert.presldent[.]info | 46.30.191[.]214 | GWY IT PTY LTD | CrownCloud | 8-Jan-2026 | 4-Sep-2026 |
| check.presldent[.]info | 45.86.163[.]87 | GWY IT PTY LTD | CrownCloud | 8-Jan-2026 | 14-Jan-2026 |
| chief.presldent[.]info | 2.58.15[.]101 | GWY IT PTY LTD | CrownCloud | 22-Nov-2023 | 9-Jul-2024 |
| it.presldent[.]info | 185.253.117[.]32 | HZ Hosting Ltd | - | 7-Aug-2025 | 13-Aug-2025 |
| tmk.natcommunzu[.]com | 193.29.57[.]159 | IP-Projects | CrownCloud | 12-Jan-2026 | 4-Sep-2026 |
| microsoft.natcommunzu[.]com | 46.30.190[.]170 | GWY IT PTY LTD | CrownCloud | 22-Jun-2025 | 4-Sep-2026 |
| storage.natcommunzu[.]com | 185.243.112[.]253 | Access2.IT Group B.V. | CrownCloud | 27-Jul-2022 | 30-Aug-2023 |
| support.natcommunzu[.]com | 185.243.112[.]220 | Access2.IT Group B.V. | CrownCloud | 14-Dec-2023 | 8-Mar-2024 |
| uz.natcommunzu[.]com | 45.67.230[.]185 | UFO Hosting LLC | - | 6-Oct-2023 | 10-Mar-2024 |
Table 6: Additional Servers Impersonating Central Asian Entities
| IP | Domain | Reseller | AS Name | Country |
|---|---|---|---|---|
| 91.132.94[.]36 | help.galkynysh[.]net kg.cwisuz[.]com | EDIS GmbH | Optimus IT d.o.o. | SI |
| 46.30.188[.]54 | www.tojiktelecomtj[.]com | CrownCloud | GWY IT PTY LTD | NL |
| 45.153.127[.]186 | gov.mpekz[.]online | EDIS GmbH | M247 Europe SRL | US |
| 185.243.114[.]238 | normativ.dushanbeidc[.]org | CrownCloud | IP-Projects | DE |
| 46.30.191[.]232 | normativ.sozandagon[.]org | CrownCloud | GWY IT PTY LTD | NL |
| 192.121.87[.]172 | data.yntymak-ord[.]com | EDIS GmbH | Trabia SRL | MD |
| 193.29.58[.]217 | link.ytnymak-ord[.]com | CrownCloud | IP-Projects | DE |
| 195.88.191[.]70 | center.yntymak-ordo[.]com | CrownCloud | GWY IT PTY LTD | DE |
| 45.153.127[.]38 | azure.adm-devon[.]com | EDIS GmbH | M247 Europe SRL | US |
| 5.183.95[.]49 | uz.adm-devon[.]com | CrownCloud | GWY IT PTY LTD | DE |
| 195.88.191[.]250 | sanly.oilgas-tm[.]com | CrownCloud | GWY IT PTY LTD | DE |
Table 7: High-Numbered Ports Observations & Subdomain Enumeration/Passive DNS
| IP | Port | Domain | Reseller | AS Name | Country | First Seen | Last Seen |
|---|---|---|---|---|---|---|---|
| 45.86.162[.]141 | 65532 | mail.postmfa[.]com | CrownCloud | GWY IT PTY LTD | NL | 9-Jan-2026 | 5-Sep-2026 |
| 45.153.127[.]99 | 65111 | center.infocomkg[.]org kg.tdtu[.]org | EDIS GmbH | M247 Europe SRL | US | 28-Jan-2026 | 5-Sep-2026 |
| 194.14.217[.]199 | - | mail.infocomkg[.]org | EDIS GmbH | M247 Europe SRL | RO | 21-Nov-2025 | 5-Sep-2026 |
| 83.242.96[.]242 | - | service.infocomkg[.]org | - | Individual Entrepreneur Iugov Denis Sergeevich | RU | 12-Apr-2025 | 5-Sep-2026 |
| 185.253.116[.]145 | - | info.tdtu[.]org | - | HZ Hosting Ltd | FR | 23-Jul-2025 | 16-Jan-2026 |
| 193.29.59[.]248 | - | ud.tdtu[.]org | CrownCloud | IP-Projects | DE | 14-Feb-2025 | 23-Jul-2025 |
| 5.183.95[.]7 | 65535 | api.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | DE | 18-Mar-2026 | 5-Sep-2026 |
| 46.30.191[.]90 | - | checkup.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 18-Mar-2026 | 5-Sep-2026 |
| 2.58.15[.]129 | - | help.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 18-Mar-2026 | 5-Sep-2026 |
| 45.86.162[.]249 | - | telecom.hpsupporter[.]com | CrownCloud | GWY IT PTY LTD | NL | 5-Jun-2026 | 5-Sep-2026 |
Summary
Malware families that Bitdefender's report treated as distinct, SpiceRAT, NodeEdgeRAT, and NomadRAT, share infrastructure at the registration level, pointing to either a single operator managing multiple toolsets or a support function shared across operators. That relationship was visible only from the network side. None of it required access to a compromised host, nor did it rely on malware samples themselves.
The targeting picture that emerges from this infrastructure, named ministries and state enterprises across five Central Asian countries dating back to at least mid-2022 suggests SilkParasite is a more recent label for an operation with much longer and wider footprint. Organizations in the affected sectors and regions can make use of the above indicators and observations to assess their own exposure.
If you're defending energy, government, or telecom infrastructure in the region, book a demo to see how these indicators track in Hunt.io.
Related Posts
Related Posts
Related Posts